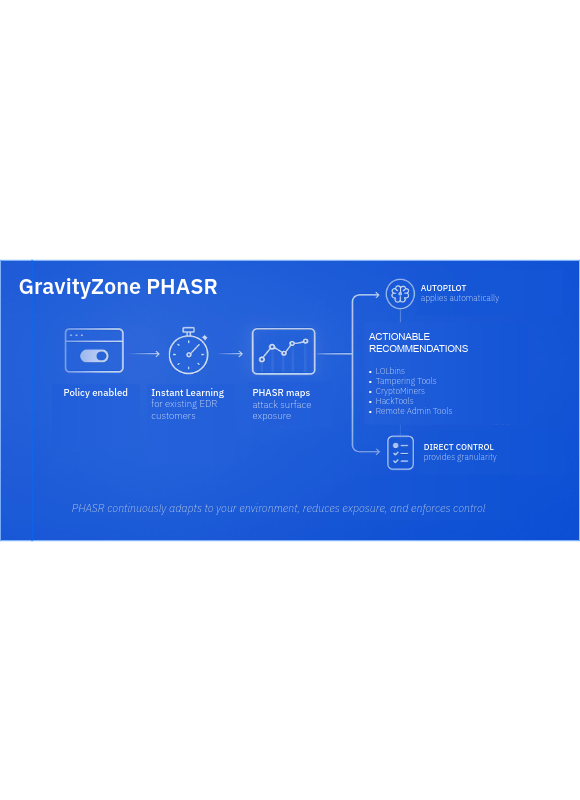
Most breaches now run on the trusted tools already installed on your endpoints — and detection alone can't stop them. GravityZone PHASR closes those attack paths proactively, and it runs standalone alongside CrowdStrike, SentinelOne, or whatever EDR/XDR you already have — no rip-and-replace required.
Modern attacks hide inside legitimate utilities like PowerShell, RDP, and WMIC — activity your detection stack can flag but rarely block. BDS sources PHASR for organizations facing these exact scenarios in the field.
The overwhelming majority of major incidents now involve abuse of native OS tools — signed, trusted, and required for daily operations. When an attacker runs PowerShell or RDP, your EDR generates an alert, not a block, because intent lives in shades of gray. Triage takes time, and attackers exploit that window to escalate, move laterally, and deploy ransomware. BDS helps organizations close this gap with proactive hardening that removes the attack path before detection is ever needed.
Lean security teams spend hours investigating alerts triggered by legitimate tool usage — trying to discern intent behind trusted activity. The volume is unsustainable, and real threats risk getting lost in the noise while analysts chase gray-area behavior.
Ask Us About a Different ApproachApplication control sounded airtight until third-party dependencies, exception sprawl, and productivity complaints made it unmanageable. Once a binary is allowlisted, it usually stays allowlisted indefinitely — leaving known policy gaps your team has quietly stopped revisiting.
Learn How PHASR Makes a DifferenceA fresh endpoint ships with more than a hundred built-in binaries attackers can abuse, and most organizations have no inventory of which tools are enabled, which are used, and which are silently exposed. You cannot reduce risk you cannot measure.
See Platform DetailsCyber insurance renewals and compliance reviews increasingly demand documented, quantifiable attack surface reduction — not just detection counts. Organizations need hardening controls that produce measurable, reportable risk reduction leadership can stand behind.
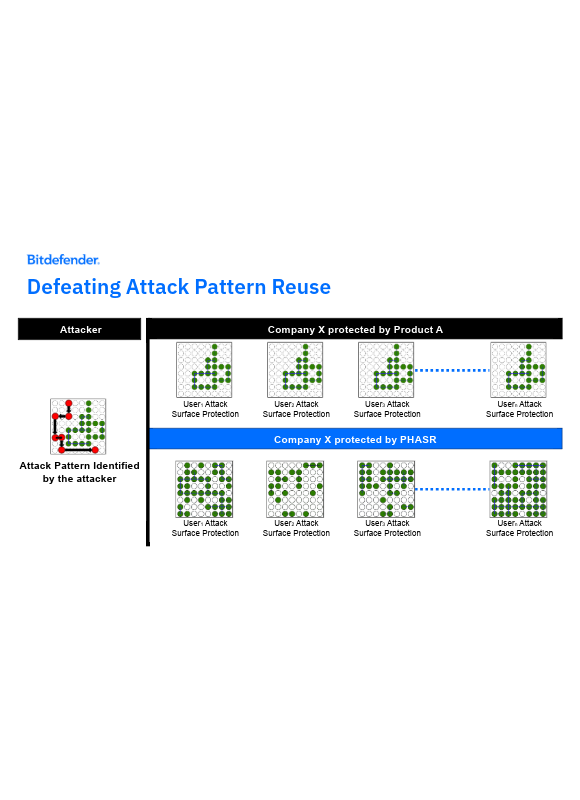
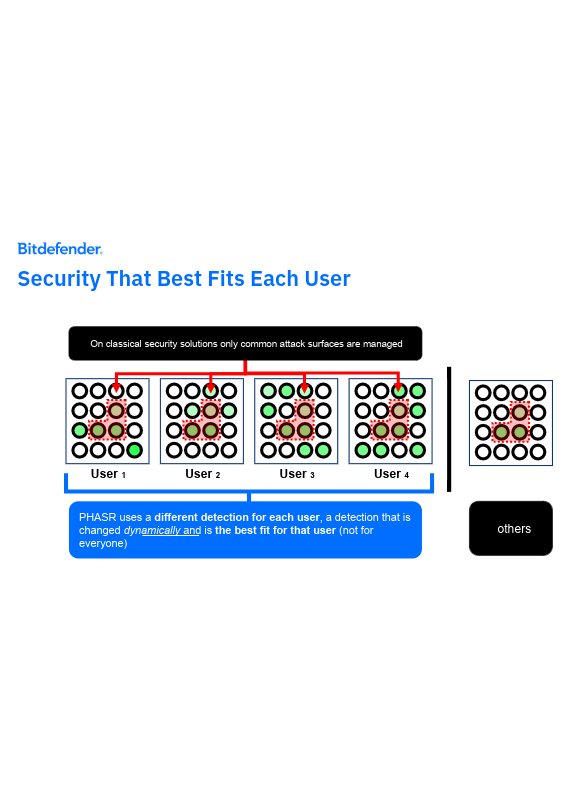
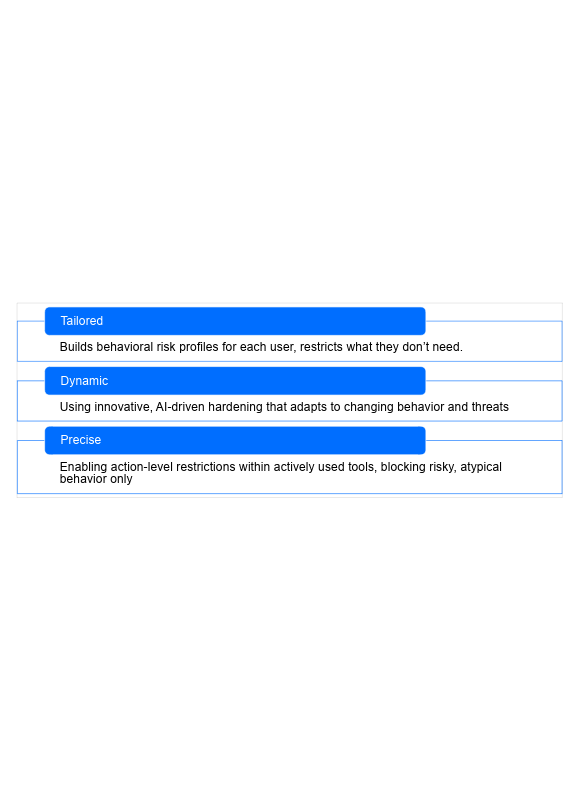
Learn How PHASR HelpsPHASR pioneered Dynamic Attack Surface Reduction: AI-driven hardening tailored to each individual user, not a static rulebook. Browse the core capabilities available through BDS.
PHASR augments what you already run — it does not replace it. BDS helps you select the right licensing path and coverage model, with one account manager from quote to activation.
PHASR's dashboard quantifies attack surface exposure and the risk reduction tied to each recommendation — before you enforce anything. It delivers the documented, reportable posture improvement that insurers, auditors, and boards increasingly require.
Running CrowdStrike, SentinelOne, or another EDR/XDR? PHASR is available standalone and compatible with any third-party detection stack — no rip-and-replace, no uninstalls, and no disruption to your existing investment.
Already on GravityZone? PHASR activates as an add-on license to GravityZone Business Security Enterprise, Bitdefender MDR offerings, and GravityZone Cloud MSP Security — and existing EDR customers can shorten the learning phase to near zero using historical data.
LOTL techniques target every operating system — not just Windows. PHASR delivers consistent, granular hardening across Windows, macOS, and Linux environments from a single policy framework.
For buyers evaluating hardening approaches — how BDS frames the decision, and what working with BDS actually looks like.
Most attack surface reduction tools rely on fixed rule sets, domain-wide exceptions, or controls that activate only after suspicious activity is detected. Anything outside the rulebook passes unchallenged. BDS helps buyers evaluate hardening options against the criteria that matter: adaptability, baselining speed, OS coverage, and administrative burden.
BDS pairs every engagement with a dedicated account manager who guides evaluation, licensing selection, and procurement — then stays your long-term point of contact. Manufacturer support runs through Bitdefender's official programs, while BDS remains your relationship-focused advisor through renewals, roadmap discussions, and future planning.
PHASR's quantified attack surface metrics give security leadership defensible evidence of proactive hardening — the control category insurers and compliance frameworks increasingly ask about by name. BDS helps you position PHASR's reporting within your renewal and audit documentation.
BDS makes sourcing PHASR simple — the right license, a clear quote, and one account manager throughout.
Independent evaluations, vendor research, and BDS's own Bitdefender credentials — the evidence layer behind this page.
"We don't measure success in transactions. We measure it in the outcomes our clients achieve because of them." - Michael Kupfer, CEO | Black Diamond Solutions
Fill out the form below and a BDS account manager will follow up within one business day with licensing guidance, pricing, and answers to your specific questions.
Have questions about PHASR licensing, compatibility, or how BDS handles sourcing? Find the most common answers below.
BDS sources Bitdefender PHASR with clear licensing guidance, competitive Gold Partner pricing, and one account manager from first question to final quote.
Your Bitdefender Gold Partner for proactive hardening — from evaluation and licensing guidance through procurement and long-term account management.
Stay informed with expert articles, cybersecurity tips, threat alerts, and practical strategies to protect your business in a rapidly evolving digital world.
View All ResourcesBlack Diamond Solutions — Cybersecurity Insights If you run a small or mid-sized business, your “attack surface” is bigger than…
By Michael Kupfer, CEO, Black Diamond Solutions If it feels like laptops, servers, and storage have gotten harder to plan…
Overview Our Cybersecurity SOC partner has flagged one newly disclosed vulnerability and one updated vulnerability impacting Cisco Secure Firewall Management…